Free Online JWT Decoder & Inspector
Decode JWT headers and payload claims instantly in your browser. Inspect expiration timestamps and token structures without exposing sensitive secrets.
How to Decode a JWT Token
Paste the token.
Copy the JWT without the word Bearer and paste it into the box. It decodes as soon as all three dot-separated parts are there.
Read the header and payload.
Both appear as indented JSON. The status bar above them shows the algorithm, Expired or Active, and the exp and iat dates in your local time.
Copy what you need.
Use the copy button on the Header or Payload panel to grab the JSON. The signature is shown as text and is not verified.
Frequently Asked Questions
Answers about decoding, verifying, expiry and keeping tokens safe.
How do I decode a JWT token?
Paste the token into the box above. It is split at the two dots, and the first two parts are Base64url-decoded into JSON. The header and payload appear right away, along with the algorithm and any exp and iat dates.
Can you decode a JWT without the secret key?
Yes. The header and payload are only Base64url-encoded, not encrypted, so anyone who holds the token can read them. The secret or private key is needed to sign or verify a token, not to read its claims, which is why tokens shouldn't carry passwords.
What is the difference between decoding and verifying a JWT?
Decoding reads the claims. Verifying recomputes the signature with the secret (HS256) or public key (RS256, ES256) to prove nobody changed them. This tool only decodes, so don't trust a token in your app until server code verifies it with a JWT library.
Is it safe to paste a JWT here?
A valid token is decoded in your browser and never sent to PixConvert. Analytics record clicks like Copy and the time a decode took. If a token is damaged, the error text is sent too, and in Chrome it can quote a few decoded characters. Expired or test tokens are the safest to paste.
What is the exp claim?
exp is the expiry time in seconds since 1 January 1970 (Unix time). This decoder shows it as a date in your local time zone and marks the token Expired once that moment has passed. A token with no exp shows Active.
Why does it say Active when the token isn't valid?
Active only means the exp time hasn't passed, or the token has no exp. The tool doesn't check the signature, nbf (not before), the issuer or the audience, so a forged or not-yet-valid token can still show Active. Check those claims yourself.
Why does my JWT show as invalid or say not enough segments?
The decoder needs exactly three parts separated by two dots. Remove the word Bearer and any quotes, and check that the copy wasn't cut off. Encrypted JWE tokens have five parts and can't be decoded without the key.
Can I decode a JWT without knowing the signing algorithm?
Yes. Decoding works the same for every algorithm, and the alg value from the header, such as HS256, RS256, ES256 or none, is shown in the status bar. You only need to know the algorithm when you verify the signature in your own code.
What's the difference between an access token and an ID token?
An ID token is always a JWT and tells your app who signed in, with claims like sub, email and name. An access token lets a client call an API and may be a JWT or an opaque string. Only JWT-format tokens can be decoded here.
Why does the signature look like random characters?
The signature is the binary output of HMAC, RSA or ECDSA, written as Base64url text. It has no readable meaning by itself and only proves the header and payload weren't changed. The decoder shows it as text and doesn't check it.
Why do names with accents look garbled?
The decoder currently reads payload bytes one at a time instead of as UTF-8, so José shows as José and emoji turn into odd symbols. The token itself is fine. Plain ASCII claims such as sub, iat and exp are not affected.
JWT Decoder for Header, Payload and Expiry
Read the header and payload of any three-part JWT as formatted JSON, see alg, exp and iat at a glance, and copy either part with one click.
Decode JWT Header and Payload to JSON
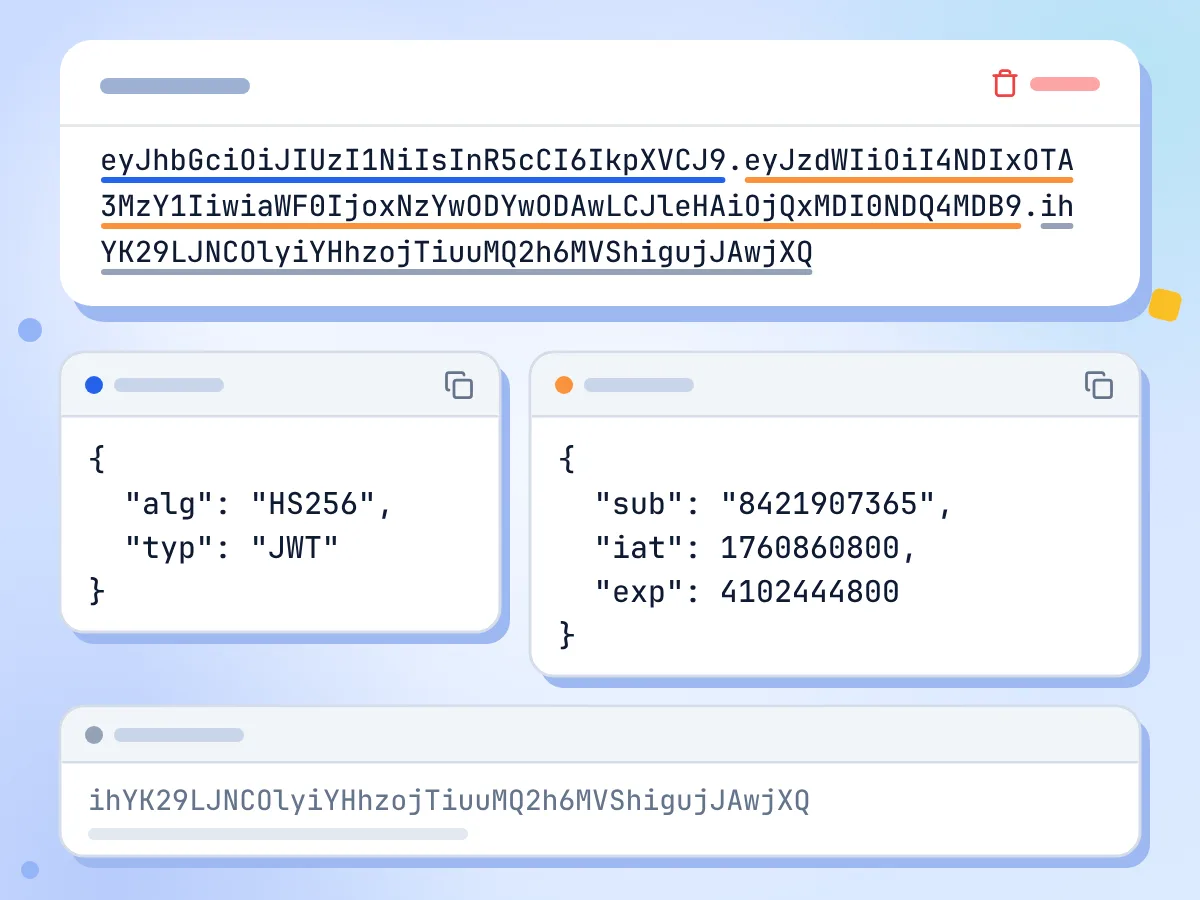
Paste a token and the header and payload appear as indented JSON while you type, with no Decode button. The raw signature is shown underneath, and each JSON panel has its own copy button.
- Decodes on every change, no button
- JSON with 2-space indents
- Copy header or payload separately
Check JWT Expiry and Algorithm
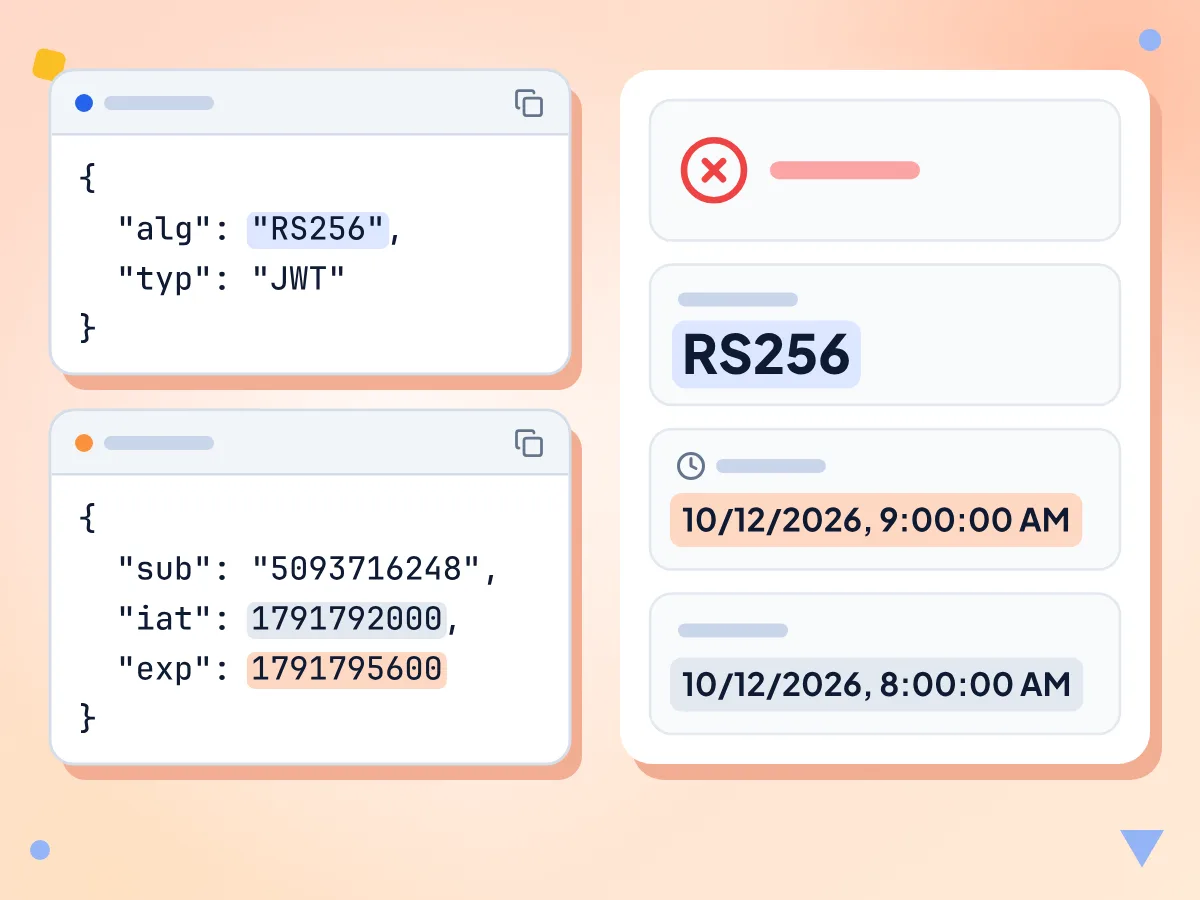
The status bar reads exp and shows Expired or Active, next to the alg from the header. exp and iat appear as dates in your local time zone, so you never convert Unix seconds.
- Expired or Active from the exp claim
- alg shown, such as HS256 or RS256
- exp and iat in local time
Decodes, Doesn't Verify
The tool never checks the signature and has no field for a secret or public key. Use it to read claims, then verify the token in your own code with a JWT library.
Base64url Handled for You
Each part is Base64url-decoded: - and _ are mapped back and missing padding is added, so tokens decode without edits. Unsigned tokens with alg none and an empty signature work too.
Free, No Account Needed
No sign-up or limit. Analytics record clicks like Copy and the time a decode took, never a valid token. A failed decode also sends the error text, which can quote part of it.
ID Tokens and Access Tokens
Decode OpenID Connect ID tokens, OAuth access tokens in JWT form and API session tokens. Encrypted JWE tokens have five parts, so they can't be read and show an error.
When You Need a JWT Decoder
Debugging an auth flow is easier when you can read what a token carries.
API Debugging
Copy a Bearer token from an Authorization header, drop the word Bearer, and paste it to see which user, roles and scopes your API receives.
- Read sub, roles and scope claims in access tokens
- Check whether a 401 error comes from an expired token
- Copy the payload JSON into a test fixture
OAuth & OIDC Development
Decode ID tokens and access tokens while you build an OAuth 2.0 or OpenID Connect login, and confirm the issuer, audience and email claims look right.
- Inspect iss, aud and email in an id_token
- Compare tokens from your test and live logins
- Read iat and exp to see how long a token lasts
Security Auditing
Review the algorithm and claims of tokens during a security check. Flag alg none, and look for personal data that shouldn't sit in a payload anyone can read.
- Spot tokens that use alg none and no signature
- Find emails or user IDs exposed in the payload
- Note long token lifetimes from the iat and exp dates
Explore More Tools
Discover other free tools that work great alongside this one
Base64 Encoder
Encode and decode Base64 strings
JSON Formatter
Format, validate and minify JSON in your browser
Hash Generator
Generate SHA-1, SHA-256 and SHA-512 hashes of text or files
URL Encoder
Encode and decode URL components
Password Generator
Generate strong, random passwords
UUID Generator
Generate random v4 UUIDs, one or up to 100 at once